
Risk management
Basic approach
Based on the principle of “Sound and Effective Corporate Governance” set forth in the CSR Charter and Code of Conduct, SCREEN has established the Risk Management Policy. In line with this policy, the Group is engaged in initiatives aimed at identifying and mitigating business risk, and the holding company implements group-wide risk management through a dedicated structure.
Risk Management Policy
Risk management structure
In order to mitigate risks with the potential to negatively impact the SCREEN Group’s corporate value, we have established a group-wide risk management structure headed by the SCREEN Holdings president and CEO, with the president of each group company responsible for managing risk at their own company.
The Group Risk Management Committee is at the center of this structure, conducting risk management operations, establishing risk management policies, identifying risks inherent in the entire Group, and monitoring their status with the aim of preventing and minimizing damage to corporate value. The committee also identifies key group risks in response to changes in the business environment each fiscal year to determine the direction of risk management and prevent these risks from materializing.
Key group risks are selected for the current fiscal year from among the items on the Group Risk List through discussion by the Group Risk Management Committee. After approval by the SCREEN Holdings president and CEO, these risks are deliberated on by the SCREEN Holdings Management Committee and finalized by resolution of the Board of Directors. Furthermore, taking an approach built around the three lines of defense,* we have designated risk managers for individual risks and their specific roles as part of a governance structure for sharing risk-related information across all levels of operations, all the way up to senior management.
* The first line of defense is borne by the group business operating companies, etc., the second line of defense by the SCREEN Holdings administrative departments and functional support companies, and the third line of defense by the internal audit departments.
● Risk management structure and roles

Enhancing risk management effectiveness
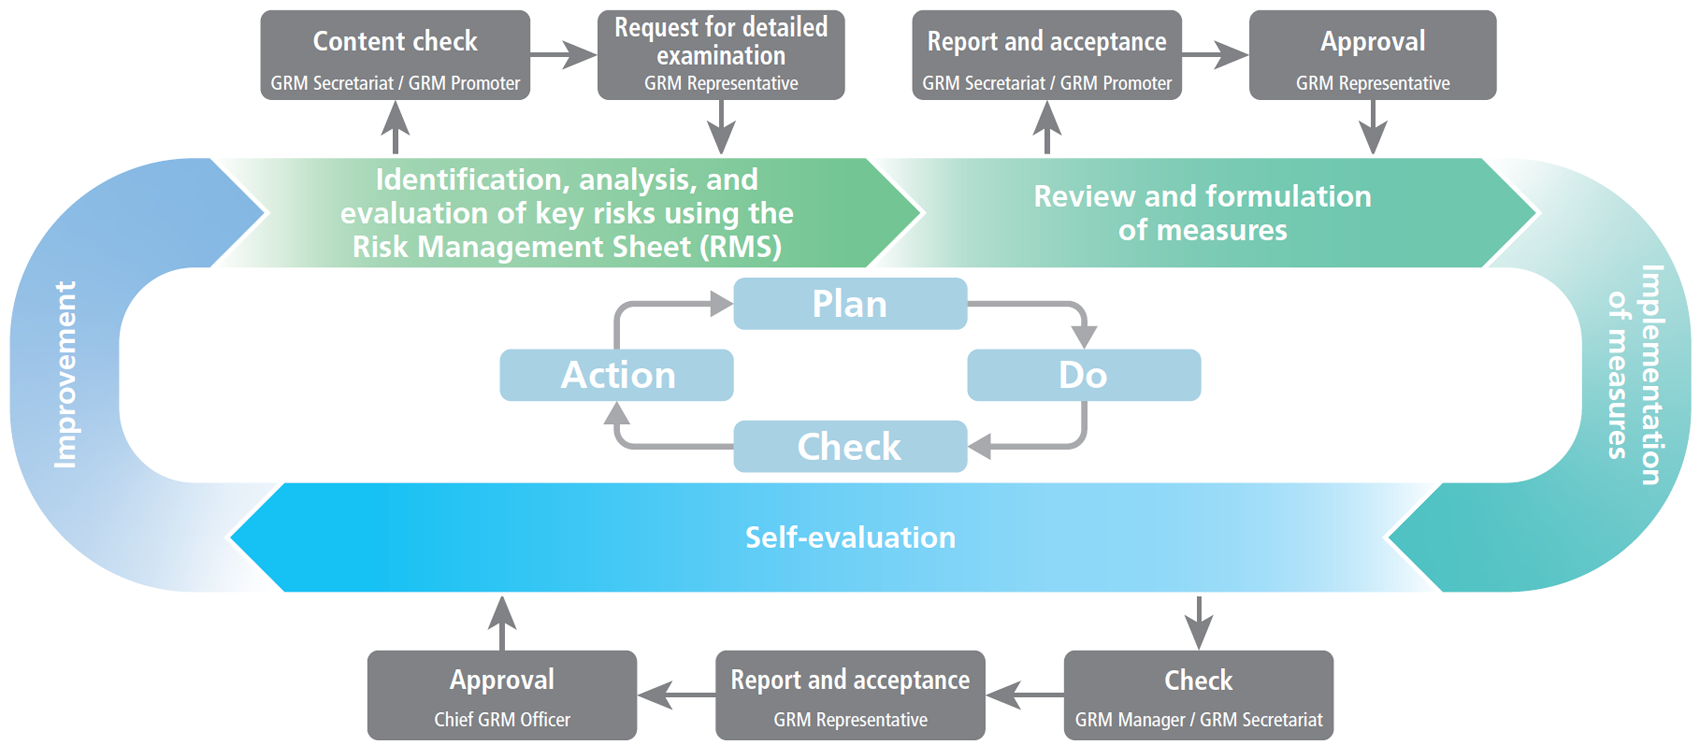
In the fiscal year ended March 31, 2026, as in the previous fiscal year, the four major business operating companies on the first line of defense and relevant members of the second line of defense held discussions, with the second line reviewing risk items, mainly key group risks, and supporting risk reduction activities. With the aim of applying consistent risk assessment standards throughout the Group, we use established criteria for assessments to further enhance risk management through such efforts as discussing the appropriateness of the first line of defense’s risk assessment results, the adequacy of specific measures, and details of related support.
●Group risk management (GRM) operational flow
●Group key risks (FY2027/03)
| Risk category | Overview of Group key risks | Mitigation measure examples |
|
1. Internal control and compliance |
●Fraudulent or improper activities within the Group (e.g., inadequate internal control, insufficient or weakening of compliance awareness) |
●Review workflows and strengthen check functions ●Fully implement thoroughgoing compliance education |
|
2. Respect for human rights |
●Harassment | ●Conduct anti-harassment training ●Operate and enhance awareness of the reporting hotline system |
|
3. Management planning, |
●Sudden changes in clients’ capital investment | ●Keep updated on the progress of clients’ capital investment plans ●Develop and implement profit improvement plans, as necessary, based on monthly profit/loss forecasts |
|
4. Technology and products |
●Decline in market share (delayed development of new technologies/products, weakened sales capabilities) |
●Formulate a product development strategy that accurately reflects client needs ●Develop and release products in line with the technology roadmap |
|
5. Safe working environments |
●Occupational accidents and injuries | ●Implement initiatives to prevent occupational accidents based on risk management |
|
6. Information systems and supplier management |
●Cybersecurity ●Supply chain security |
●Implement role-based training and cyber incident drills ●Perform assessments of group companies and suppliers ●Conduct 24/7 threat monitoring |
| 7. Development of next-generation leaders | ●Delays in successor development | ●Implement internal training programs and talent reviews to develop next-generation business leaders |
Business continuity plans
The Group strives to stay well prepared for emergencies, such as natural disasters and pandemics, with top priority placed on the safety of employees and their families. To ensure that we can continue to fulfill our responsibility to supply products and services even in the event of a catastrophic disaster, we have acquired certification under ISO 22301, an international standard for business continuity management systems, and have in place an effective system for implementing business continuity plans (BCPs) to quickly resume business operations.
Emergency system
Our safety confirmation system is designed to promptly check the safety of employees in an emergency, while our disaster information sharing system helps us grasp and share the extent of damage from a disaster quickly and accurately. In addition to practical training using these systems, we conduct regular, systematic drills to enhance our overall disaster response capabilities. We are also strengthening our emergency communication system by using satellite communications to prepare for potential communication disruptions. In the fiscal year ended March 31, 2026, we held a disaster response drill simulating a Nankai Trough earthquake, helping strengthen the Group’s overall business continuity capabilities.
Strengthening the manufacturing base
At our operating sites in Japan, we undertake a variety of measures to strengthen the manufacturing base, including evaluating seismic resistance, reinforcing buildings, dismantling aging facilities, immobilizing equipment and facilities, and adopting seismic-resistant machinery and equipment. Based on lessons learned from past large-scale disasters and supply chain interruptions, we endeavor to put in place production systems in which production sites and parts suppliers in and outside Japan can be used to cover for one another if necessary in order to prevent significant damage to our business from such events. At the Hikone Site in Shiga Prefecture, which produces semiconductor manufacturing equipment, we have taken earthquake countermeasures and completed the installation of flood barriers. At other sites, we are advancing measures tailored to specific site characteristics, including systematic flood countermeasures.
Stable procurement
We are also reinforcing BCPs in procurement, including introducing a system to check the impact on suppliers after a disaster, finding alternatives to critical parts, and diversifying procurement sources and logistics partners. To extend these activities throughout the value chain, we are enhancing the field service structure to support clients affected by disasters and conducting surveys on suppliers’ BCP readiness.
Strengthening information security
SCREEN regards cyberattacks and other information security risks as a key management issue. Under the leadership of the SCREEN Holdings head of digital transformation strategy, we continuously strengthen information security across the SCREEN Group by formulating and implementing group-wide rules and an IT roadmap, which sets forth long-term policy.
Cyberattack methods and information security risks are constantly evolving. To respond quickly to these changes, we operate around-the-clock global monitoring to detect and respond to suspicious behavior on computers, servers, and other devices. Recognizing that protecting information security is our social responsibility, we take measures to ensure smooth business continuity, including exercises simulating responses to potential incidents. In addition, we work to raise awareness by providing annual information security training reflecting the latest developments to all officers, employees, temporary staff, and other personnel.
To strengthen information security, the SCREEN Group has established a risk management framework. Through this framework, taking a comprehensive view that encompasses risk management in the supply chain, we work to maintain a level of security that complies with relevant national laws and regulations and industry group security standards.